Solutions by sector
Government & Finance
Interception-proof workplaces and certified one-way transfer for authorities, banks and organisations handling classified or market-sensitive information.
- Environments
- 22
- Architecture patterns
- 16
- Products used
- 63
Authorities and financial institutions handle information whose leakage carries national or market-wide consequences. Fibersystem equips them with the same certified protection we deliver to the armed forces.
For classified and sensitive environments
- TEMPEST-certified workplaces stop electromagnetic eavesdropping (RÖS) on computers, monitors, printers and phones – the attack that firewalls cannot see.
- Data diodes enable secure one-way publishing and log collection between security domains.
- Secure video conferencing for meetings that must stay in the room.
Customers include the Swedish Police, government agencies and financial institutions. All products are designed and developed in Stockholm, with a certified secure supply chain.
Environments
Used in these environments
22 real installations, filterable by area
Showing all 22 environments
- 01TEMPEST/RÖS
Embassy or mission in an urban setting
The environment offers no inherent protection: there is no controlled zone to count on. - 02KVM & VTC
Emergency call centre
Round-the-clock operation with no maintenance window: whatever is installed has to be replaceable while it runs. - 03Data diodes
Log export to a SOC
The one flow where the diode is cheaper and simpler than the alternative — which is why it is almost always the right first installation. - 04TEMPEST/RÖS
Registry function
Paper is a zone exit that no network diagram shows. - 05TEMPEST/RÖS
Briefing room
A shared room is harder than a single workstation, and the bridge for an external client is a deliberate compromise that must be decided in advance. - 06Data diodes
Publishing between classification domains
The hard part is not the transport but the release decision: who decides that this document may leave, and how is that recorded. - 07KVM & VTC
Boardroom in a protected company
The people in the room have decision authority and no security training, and the equipment has to work without either. - 08Data diodes
Patch distribution into a closed network
The direction runs towards the protected side, which inverts every assumption the other flows rest on. - 09KVM & VTC
Embassy meeting room
Every path is open at once: image, sound, USB and the network — and the room is used daily by people who are not technicians. - 10Data diodes
File lock and media transfer
This is where people work around the protection when it becomes inconvenient — the design has to assume that. - 11TEMPEST/RÖS
Agency office in a shared building
The power supply belongs to the property, not to the tenant — and conducted emission does not need to pass through the wall. - 12KVM & VTC
Remote workplace towards a classified environment
Moving the computer moves the problem; it does not remove it, because the desk becomes an extension of the computer. - 13TEMPEST/RÖS
Research laboratory
Results have to leave the zone continuously, which makes the outflow the design problem rather than the workstation. - 14Data diodes
Financial market data
Multicast passes natively, which is exactly the distribution model market data uses. - 15TEMPEST/RÖS
Negotiation room in the private sector
The threat is commercial rather than state-level, but the room is used by people who have never been briefed. - 16Data diodes
Evidence and forensic chain
Transaction logs and per-transfer hash verification are what make the chain documentable. - 17TEMPEST/RÖS
The bank trading desk
Many screens, many networks and no tolerance for a switching delay measured in seconds. - 18TEMPEST/RÖS
Home workplace for classified work
A home cannot be zoned. A thin client reduces the consequence but does not create a zone. - 19Data diodes
Replacing an air gap
Mapping the flows comes before choosing the product — the air gap is upheld by manual work that is rarely counted as cost. - 20KVM & VTC
Shared AV equipment in a common meeting room
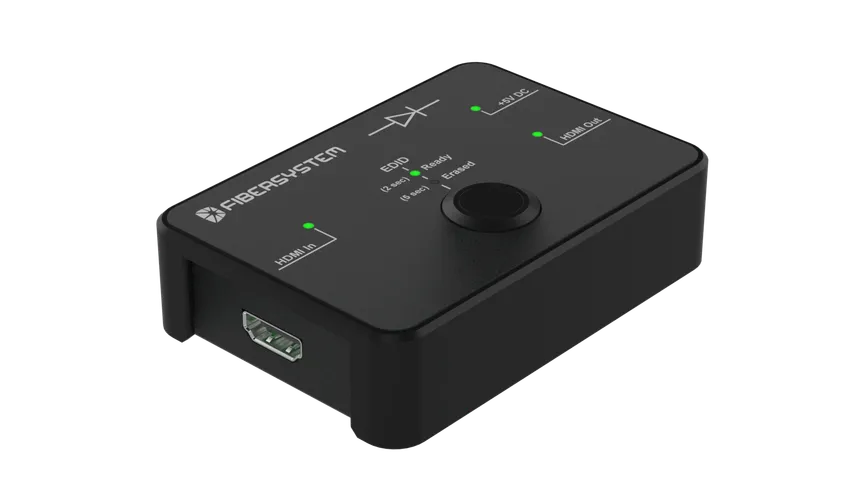
The EDID table in the display is overwritten by the fourth computer connected, so the fifth gets a black screen — which is exactly the inconvenience that breeds the workaround. - 21Fiber & OT
Link between security domains
The only environment where the absence of an electrical signature is the main argument rather than a side effect. - 22Data diodes
Presentation across a domain boundary
The shared display is the only common component — and therefore the only channel connecting the domains.
In the catalogue
Most specified for this sector
The products that recur most often in the environments above.
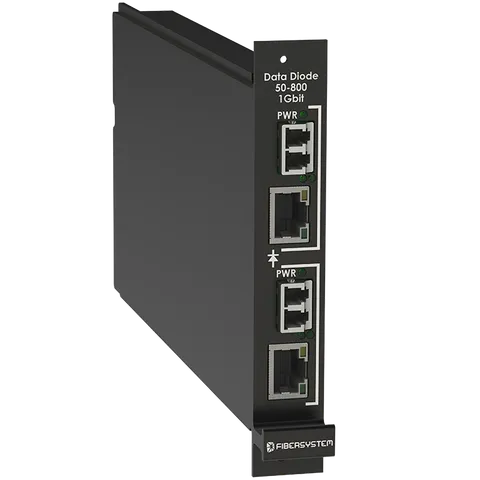
TEMPEST Level A · RÖS U1
Data Diode Secure 1 Gbit MM TEMPEST
- Data rate
- 1 Gbps
- Wavelength
- Multimode 850 nm
- Input, LC
- 1000 BaseSX
Product no 60-00-7303
Standard
Data Diode Secure 1 Gbit SM
- Data rate
- 1 Gbps
- Wavelength
- Singlemode 1310 nm
- Input, LC
- 1000 BaseLX
Product no 60-00-8362
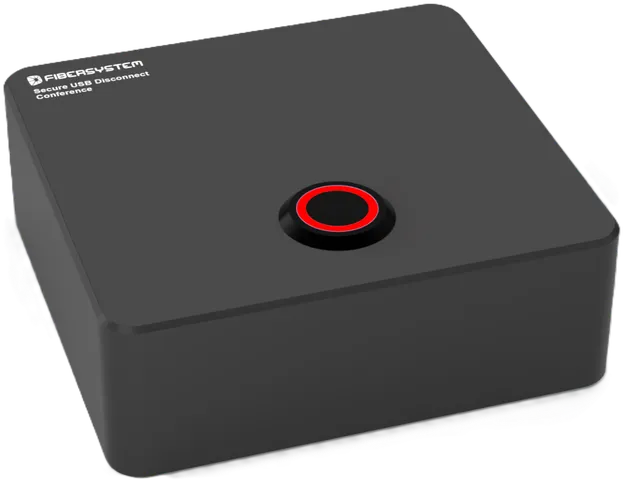
Standard
Secure USB Disconnect Conference
- Dimensions
- 38 x 100 x 100 (HxWxD) mm
- Weight
- 300 Gram
Product no 60-00-0235
How it is built
Architecture patterns
Pattern DD-B · Log export and evidence retentionSyslog passes natively without middleware, and the chain of custody gets stronger as a side effect.
- One-way path
- Data path
- Path that does not exist
- DD-BLog export and evidence retentionSyslog passes natively without middleware, and the chain of custody gets stronger as a side effect.
- KV-CThe display as a pure receiverHDMI is not one-way: DDC runs in both directions, and EDID is a shared, writable object.
- TE-AThe single workstation in a Level A zoneThe indivisible zone: every device in the chain carries the level, and the weakest one sets it.
- TE-DThe briefing room with a shared displayThe bridge for an external client is a deliberate compromise, decided in advance and written down.
- DD-EFile lock between domainsFrom a USB stick to a one-way transfer, with the human decision made explicit rather than assumed.
Government & Finance
Your sector not listed?
The threat model matters more than the label. Describe your environment and we match it with certified hardware – or build what is missing.
Verified credentials
All certifications- Government of SwedenSupplier to Swedish authoritiesPolice · FMV · FOI
- NATOCertified TEMPEST supplierSDIP-27 · Level A & B
- Swedish Armed ForcesM-numbered equipmentMain supplier, Total Defence
- ISO 9001 14001ISO certifiedQuality & environmentDownload certificate (JPG)
- SOFFDefence industry memberExport control frameworks
- Made in SwedenDesigned & built in StockholmSecure supply chain